
Physical security & cybersecurity
Understand the risks to your facilities, people, systems, and information.
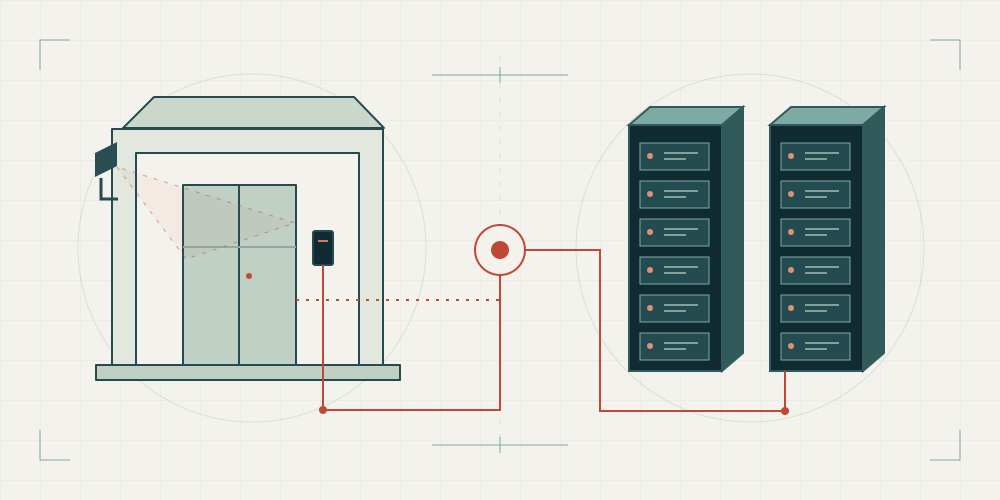
Prometheus Global provides physical security and cybersecurity assessments for commercial organizations and government agencies. We help you understand your current security posture, identify weaknesses, and decide where improvements will have the greatest value.
How physical and cyber risks connect
The systems used to protect a facility can themselves become targets of cyberattacks. Compromised access controls, cameras, or monitoring systems can weaken physical protection. Unauthorized physical access to equipment can, in turn, bypass or undermine cybersecurity controls.
Prometheus Global brings expertise in both disciplines. We assess the connections between physical and cyber defenses alongside the individual controls, helping you identify gaps and prioritize improvements that work together.
Physical security assessments
Evaluate the safeguards that protect your facilities and personnel. We review physical access controls, security procedures, and the way those measures work together in your operating environment.
The assessment identifies gaps in physical protection and provides recommendations to strengthen security. We agree the scope and assessment methods with your team before work begins.
Cybersecurity assessments
Examine the security of your networks, systems, and information. Depending on the agreed scope, an assessment can include internal and external network assessments, security architecture reviews, and analysis of system configurations and existing controls.
We combine technical analysis with expert review to identify vulnerabilities, misconfigurations, and weaknesses in your defenses. Findings explain the risks and the steps your team can take to address them.
Assessments informed by regulatory experience
Our team brings direct experience in developing security regulations and guidance, creating inspection programs, conducting inspections, and enforcing requirements. That background helps us evaluate how security measures are implemented and documented, and how they support the requirements relevant to your organization.
Assessments can be aligned with applicable regulatory requirements and selected security frameworks. Our work covers U.S. and EU requirements, NERC CIP, and federal FISMA programs, as well as nuclear cybersecurity and physical security worldwide. We agree the scope and assessment criteria with you, then connect findings with practical steps to close gaps. Learn more about our regulatory and compliance services.
A clear scope and practical findings
Each engagement starts with your priorities, the environment to be assessed, and an agreed plan. We coordinate the work with your team and communicate significant findings as they emerge.
Our assessment reporting connects the findings with decisions and next steps:
- An executive summary of the principal risks and findings.
- Detailed findings for the physical or technical areas assessed.
- Recommended improvements and priorities for remediation.
Physical security and cybersecurity can be assessed separately or together, according to your organization’s needs. In either case, we consider the dependencies that matter to the agreed scope.
What would you like to assess?
Talk with our team about your facilities, systems, and security priorities.
Discuss an assessment →